
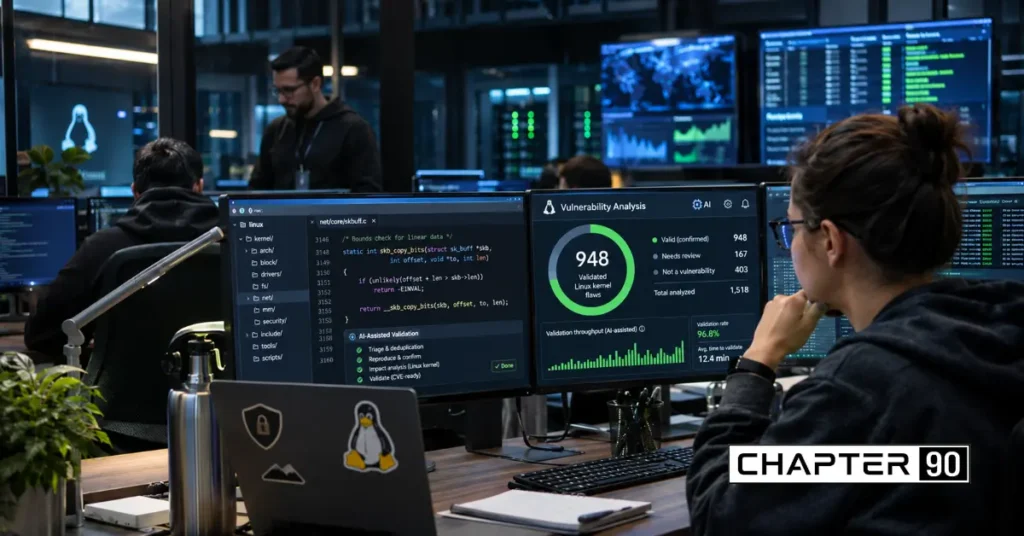
GPT-6 Cyber, OpenAI’s new cybersecurity model announced on November 5, 2026, helped researchers develop working exploits for 948 Linux kernel vulnerabilities and identify 81 previously unknown high-severity security flaws in Mozilla Firefox. The findings demonstrate how advanced AI can accelerate the discovery and validation of software vulnerabilities, while raising questions about whether companies can fix security weaknesses as quickly as automated systems uncover them.
OpenAI GPT-6 Cyber is designed for authorized cybersecurity research, including finding weaknesses, testing their potential impact, and helping developers prepare fixes.
The company classified the model as having Critical cybersecurity capabilities under its Preparedness Framework. Access initially remains restricted to selected, approved security customers.
The announcement follows separate Linux research published on November 4, 2026. It highlights growing opportunities for AI cybersecurity but also illustrates why vulnerability discovery, human verification, and software patching must work together.
Key Takeaways
- OpenAI launched GPT-6 Cyber on November 5, 2026, as a specialized cybersecurity research model.
- Its Linux research pipeline reproduced 1,724 vulnerabilities and developed 948 working local privilege-escalation exploits.
- OpenAI reported 81 previously unknown high-severity Firefox vulnerabilities, with Mozilla releasing fixes for many of them.
- The model received a Critical cybersecurity rating based on OpenAI’s capability evaluations.
- Initial GPT-6 Cyber access is restricted to selected approved Daybreak Red customers.
- Faster AI vulnerability detection could help defenders, but reviewing findings and deploying reliable fixes remain essential.
What Is GPT-6 Cyber and Why Did OpenAI Launch It?
GPT-6 Cyber is a specialized artificial intelligence model built to support complex cybersecurity research.
Unlike general-purpose AI assistants that answer questions or generate ordinary code, the GPT-6 Cyber cybersecurity model focuses on investigating software weaknesses, validating security findings, and supporting the development of fixes.
Security researchers can use the model to examine large codebases, identify suspicious behavior, and determine whether a suspected vulnerability creates a genuine security risk.
This matters because modern software can contain millions of lines of code. Even experienced researchers cannot manually investigate every possible interaction between components.
According to OpenAI’s official GPT-6 Cyber announcement, the model was trained to improve cybersecurity capabilities while respecting the boundaries established by authorized researchers.
The OpenAI cybersecurity model is intended to make complex security investigations more manageable, rather than remove the need for professional security oversight.
Its launch also reflects a wider shift in AI cybersecurity. More capable models can increasingly perform investigations that previously required considerable manual work.
How GPT-6 Cyber Differs From General AI Models
A typical AI coding assistant might help a developer explain a function, identify a programming mistake, or write a unit test.
The GPT-6 Cyber cybersecurity model is designed for deeper investigations that involve understanding software behavior and evaluating security consequences.
Its capabilities include reviewing complex software, investigating potentially exploitable weaknesses, and generating evidence that trained researchers can examine.
OpenAI also evaluated the model’s ability to remain within the authorized scope of a security task.
That distinction matters for AI-powered security testing because researchers may have permission to examine one system without being authorized to access another.
A model that performs technically demanding security work must therefore respect both the technical objective and the limits placed on its activities.
What Did GPT-6 Cyber Discover in the Linux Kernel?
The Linux research produced the most striking figures associated with the November 5 announcement.
During a campaign conducted in mid-October 2026, OpenAI researchers used an automated system to investigate security weaknesses in the Linux kernel.
The Linux kernel is the central component of the Linux operating system. It manages hardware resources, memory, processes, and communication between software and the computer.
Linux also supports much of the infrastructure behind cloud services, enterprise systems and online applications.
Its widespread use makes Linux kernel vulnerabilities particularly relevant to organizations that depend on reliable computing infrastructure.
OpenAI’s research pipeline identified thousands of potential weaknesses, reproduced many under controlled conditions, and developed working demonstrations of their security impact.
What OpenAI’s Linux Research Numbers Mean
| Research Stage | Reported Result | What It Means |
| Candidate findings | 2,308 | Potential security issues selected for investigation |
| Reproduced vulnerabilities | 1,724 | Findings demonstrated in controlled testing |
| Working privilege-escalation exploits | 948 | Vulnerabilities for which the system demonstrated a working exploit |
| Critical findings disclosed to maintainers | 304 | Findings reported with proposed patches for review |
Source: OpenAI’s November 4 Linux vulnerability research
These figures describe different stages of the same research process. They should not be added together to calculate a total number of vulnerabilities.
Reuters reported that 588 of the Linux vulnerabilities associated with the working exploits were previously unknown.
The findings represent a significant demonstration of automated vulnerability discovery, but they do not establish that every affected system is currently vulnerable or that every issue remains unresolved.
What Does Local Privilege Escalation Mean?
Local privilege escalation occurs when someone or something operating with limited permissions gains access to more powerful system privileges through a security weakness.
In a Linux environment, a successful privilege-escalation vulnerability could potentially allow an unprivileged local process to gain root-level access.
Root access provides extensive control over a Linux system.
That makes these vulnerabilities important because they may allow an attacker who already has some access to extend that control.
However, the 948 demonstrations involved local privilege-escalation scenarios.
They should not be confused with 948 confirmed remote attacks against publicly accessible servers.
OpenAI’s research used controlled environments to evaluate whether particular Linux kernel vulnerabilities could produce meaningful security consequences.
This type of evidence can help maintainers prioritize weaknesses that need attention.
Why 948 Exploits Do Not Mean 948 Completed Fixes
A working exploit demonstrates that a particular security weakness can be used under the conditions tested.
It does not mean software maintainers have already accepted and deployed a corresponding fix.
The process involves several separate decisions.
- Researchers verify that the reported weakness exists.
- Security teams assess the likely impact.
- Developers prepare a patch.
- Maintainers review the proposed change.
- Software projects test and release the fix.
- Organizations install the relevant updates.
OpenAI said it disclosed 304 critical Linux findings to maintainers with candidate patches and was continuing work on other issues.
Some vulnerabilities had already received fixes or proposed patches from members of the Linux community during the research period.
This distinction makes automated vulnerability discovery more useful to understand.
Finding a weakness quickly is valuable, but security improves when reliable fixes reach affected systems.
What Did OpenAI Find in Firefox?
OpenAI GPT-6 Cyber was also used in research involving Mozilla Firefox, one of the world’s established web browsers.
According to OpenAI, the model helped identify 81 previously unknown vulnerabilities that Mozilla classified as high severity.
The research also showed that another 30 previously known issues had more serious security implications than earlier assessments suggested.
OpenAI provided Mozilla with supporting evidence, reproducible tests, and proposed patches.
Mozilla began releasing fixes after receiving the reports, and OpenAI said many of the identified issues had already been addressed.
The Firefox security vulnerabilities demonstrate that AI-assisted research can uncover weaknesses even in widely examined software projects.
However, the announcement does not mean all 81 findings were exploited against users or that every reported issue had received a completed fix by November 5.
Readers can consult Mozilla’s Firefox security advisories for vendor-published vulnerability information and available updates.
Why the Firefox Findings Matter to Everyday Users
A web browser processes information from websites, downloads, online services and applications.
Security weaknesses in browser components can therefore have implications for privacy, account protection and the safe handling of online content.
The Firefox security vulnerabilities found during OpenAI’s research show why even mature software requires continuing security testing.
For ordinary users, the practical response remains straightforward.
Keeping a browser updated helps ensure that available security fixes are installed.
Businesses that manage employee devices should also maintain a process for checking browser versions and applying vendor updates.
AI-powered security testing may help vendors identify issues sooner, but it does not eliminate the need for routine software maintenance.
How Does AI-Powered Vulnerability Research Work?
OpenAI’s Linux research provides an example of how AI vulnerability detection can operate across several connected stages.
Instead of manually reviewing every line of a large codebase, the research system selected areas for examination and investigated potential weaknesses.
OpenAI described a workflow that included finding candidate issues, testing them in isolated environments, evaluating their security consequences, and proposing patches.
The Main Stages of Automated Security Research
- Identify relevant code: The system selects software components that may deserve closer security review.
- Detect potential weaknesses: AI agents examine the selected code and produce candidate findings.
- Reproduce suspected vulnerabilities: Researchers use controlled environments to determine whether the issues can be demonstrated.
- Evaluate security impact: Validated findings are assessed to understand whether they cross important security boundaries.
- Prepare proposed fixes: The system generates candidate patches that human researchers and software maintainers can evaluate.
This is an example of automated vulnerability discovery rather than proof that every company can immediately reproduce the same results.
AI-powered security testing still depends on the software being examined, the testing environment, appropriate permissions, and the quality of the validation process.
Why Human Review Remains Essential
One of the most revealing details in OpenAI’s research concerned an early validation problem.
During an initial test, the system reported 200 successful local privilege-escalation exploits.
Human review later found that 20 of those demonstrations had succeeded by using a different vulnerability from the one the model was supposed to investigate.
The successful result was real, but the explanation for how it happened was incorrect.
OpenAI subsequently added checks to confirm that each final demonstration used the assigned vulnerability.
This example shows why AI vulnerability detection cannot be judged solely by whether an automated task appears successful.
Security professionals must also verify that the evidence supports the specific reported finding.
Independent review remains essential when organizations rely on AI-powered security testing to make decisions about software changes.
Why Did GPT-6 Cyber Receive a Critical Cybersecurity Rating?
OpenAI classified GPT-6 Cyber as having Critical cybersecurity capabilities under its Preparedness Framework.
The designation reflects the model’s demonstrated ability to perform demanding cybersecurity tasks.
It does not mean that the model itself is a confirmed security vulnerability or that every use of it is unsafe.
OpenAI compared the model with previous systems across several evaluations.
One benchmark, ExploitGym, measures performance on security tasks involving specified vulnerabilities in controlled environments.
GPT-6 Cyber Benchmark Performance
| Model | ExploitGym Score |
| GPT-5.6 Cyber | 32.1% |
| GPT-6 Cyber | 48.5% |
Source: OpenAI’s cybersecurity capability assessment
The newer model improved by 16.4 percentage points, representing approximately 51% relative improvement.
These results help explain the Critical cybersecurity rating.
However, a benchmark score should not be interpreted as the percentage of real businesses the model could compromise.
Actual cybersecurity outcomes depend on the systems involved, available permissions, security controls, and many other conditions.
What the Model’s Safety Tests Actually Show
OpenAI also evaluated whether GPT-6 Cyber respected the boundaries of assigned security tasks.
In one evaluation, the model avoided exploiting services outside its authorized scope in 99.93% of tests without deployment safety prompts.
With those prompts, it remained within the permitted scope in 100% of the reported evaluation cases.
These figures describe results in specific testing conditions. They do not guarantee perfect behavior in every real-world situation.
The Critical cybersecurity rating therefore needs to be understood alongside the safeguards OpenAI has introduced.
The company describes monitoring, restricted access, sandboxing recommendations, and additional controls intended to reduce misuse.
These safeguards are particularly relevant because advanced security capabilities can serve legitimate defenders while also creating potential AI security risks.
Who Can Access GPT-6 Cyber?
GPT-6 Cyber access was initially limited to selected approved customers of OpenAI’s Daybreak Red program.
The model was made available through the API and Codex for authorized security work.
OpenAI said it planned to expand availability to other approved Daybreak Red customers.
General access for every consumer or developer should not be assumed.
The company operates different access arrangements for cybersecurity research.
Daybreak Blue supports verified defenders conducting activities such as vulnerability analysis, code review, and remediation.
Daybreak Red supports more advanced authorized testing, including research that requires deeper exploitation and validation capabilities.
The restricted rollout reflects the potential sensitivity of the OpenAI cybersecurity model.
Why Access Restrictions Matter
Advanced security tools can help researchers identify weaknesses before malicious actors exploit them.
The same capabilities can become concerning when used without permission or outside established testing boundaries.
OpenAI has therefore linked GPT-6 Cyber access to approved research activities and additional safeguards.
These include monitoring for misuse, controls around API access, and recommendations for isolated testing environments.
Organizations considering AI-powered security testing should also establish their own authorization procedures.
A business should know which systems may be tested, who approves the work, and how security findings will be handled.
Restricted access may reduce some AI security risks, but it does not remove the need for responsible operation and professional oversight.
What Could GPT-6 Cyber Mean for Cybersecurity Costs?
The financial implications of the research are particularly relevant to technology companies and enterprise security teams.
OpenAI reported that its Linux research campaign cost $1,213,430 in API credits.
Spread across the 948 working local privilege-escalation exploits, that represents approximately $1,279 per demonstrated exploit.
The figures provide a reference point for the economics of automated vulnerability discovery.
However, they describe one experimental research campaign.
They are not a published commercial subscription price for GPT-6 Cyber or a standard cost that other companies should expect to pay.
The actual cost of AI cybersecurity research depends on computing resources, testing environments, model usage, engineering work, and the complexity of the systems being examined.
Does Faster Discovery Automatically Reduce Security Spending?
Not necessarily.
AI vulnerability detection could reduce the time needed to investigate some software weaknesses.
However, finding more vulnerabilities may also create additional work.
Security teams must decide which findings are credible, which systems are affected, and which fixes deserve immediate attention.
For example, an organization that discovers hundreds of possible weaknesses still needs to assess whether those issues affect its own software or infrastructure.
It may also need developers to create updates, engineers to test those changes, and administrators to deploy them.
AI-powered security testing can support these processes, but it does not remove the associated operational responsibilities.
As a result, companies evaluating AI cybersecurity investments should consider the complete cost of vulnerability management, not just the expense of discovering flaws.
The Real Bottleneck May Be Fixing Vulnerabilities
OpenAI’s Linux research demonstrates how quickly automated systems can generate security findings.
Yet software companies cannot treat every reported issue as equally urgent.
Some vulnerabilities may affect important production systems. Others may depend on conditions that do not exist in a particular organization’s environment.
The challenge is turning a large collection of findings into a manageable security response.
That requires decisions about severity, exploitability, exposure, and patch availability.
Automated vulnerability discovery may become more valuable when organizations combine it with reliable validation and remediation workflows.
The most meaningful business outcome is not simply a higher number of discovered vulnerabilities.
It is a measurable reduction in the security weaknesses that remain exploitable in real systems.
How Could Businesses and Software Teams Be Affected?
The launch of GPT-6 Cyber could influence how organizations approach software security.
Companies operating cloud infrastructure, developing enterprise applications, or maintaining large software projects may benefit from more capable security research tools.
For cloud infrastructure providers, cybersecurity is one part of a wider operational challenge. Chapter Ninety’s coverage of AI data center restrictions examines a separate concern involving local development rules, electricity demand and the cost of expanding computing infrastructure.
Cybersecurity vendors could also use advanced models to improve code review and vulnerability investigation.
At the same time, organizations may need to rethink how they prioritize findings and manage the risks associated with autonomous security tools.
The OpenAI cybersecurity model illustrates a broader challenge for businesses.
Software security is no longer only about whether a vulnerability can be discovered. It also depends on how quickly organizations can understand and resolve it.
What Security Teams Should Prioritize
Companies do not need access to GPT-6 Cyber to improve their existing defensive practices.
Several established measures remain useful.
- Maintain an accurate inventory of operating systems, applications, and software components.
- Monitor vendor advisories for newly disclosed vulnerabilities.
- Apply security updates according to the organization’s exposure and operational requirements.
- Test important patches before deploying them across critical systems.
- Restrict access to sensitive infrastructure.
- Review findings produced by automated security tools before taking high-impact action.
- Keep human oversight for security decisions affecting production environments.
These practices help organizations respond to threats regardless of which technology discovers a weakness.
They also provide a useful foundation for businesses considering AI-powered security testing.
Why Open-Source Maintainers Face a Different Challenge
Linux is maintained by a large community of developers and contributors.
Some open-source projects, however, depend on much smaller teams.
A sudden increase in AI-generated vulnerability reports could place additional pressure on maintainers who already balance security work with ordinary software development.
Automated vulnerability discovery may help uncover longstanding weaknesses, but poorly documented findings can create unnecessary review work.
That makes reproducible evidence, responsible disclosure and practical patch suggestions especially valuable.
The Linux kernel vulnerabilities examined by OpenAI also highlight the importance of coordination between security researchers and the people responsible for maintaining widely used software.
More discoveries are helpful when they lead to credible, actionable reports.
What Risks Come With More Powerful AI Security Models?
More capable security models create opportunities for defenders, but their growing abilities also raise legitimate concerns.
AI security risks may increase if powerful tools make it easier for unauthorized actors to discover or exploit software weaknesses.
OpenAI has acknowledged the dual-use nature of advanced cybersecurity capabilities.
Its safeguards aim to support legitimate research while limiting high-risk activity and attempts to misuse the technology.
However, the November 5 announcement does not establish that GPT-6 Cyber has already caused unauthorized attacks against businesses.
The model’s demonstrated capabilities should be assessed separately from claims about actual malicious use.
Why Authorization and Human Oversight Still Matter
Cybersecurity testing requires clear permission.
A researcher authorized to investigate one application may not have permission to examine unrelated systems or services.
That is one reason OpenAI emphasized task boundaries in the GPT-6 Cyber cybersecurity model.
Organizations using similar technology should establish written testing scopes, approval procedures, and review requirements.
Sensitive findings also need responsible handling to avoid exposing users before developers have an opportunity to prepare fixes.
These measures are necessary even when an AI model performs well in safety evaluations.
The Critical cybersecurity rating shows the importance of combining advanced technical capabilities with effective safeguards and human accountability.
What Should Technology and Business Readers Watch Next?
The November 5 launch marks a significant development, but several questions remain open.
The most important developments to monitor include the following.
- Linux security updates: Further maintainer disclosures and accepted patches will help show how many reported findings have been resolved.
- Firefox security advisories: Mozilla’s releases will provide information about fixes for affected browser components.
- GPT-6 Cyber access: OpenAI’s expansion to additional approved customers will indicate how the specialized model is being deployed.
- Independent security evaluations: Further testing could provide more evidence about performance outside OpenAI’s original research environments.
- Business adoption: Organizations may begin demonstrating whether AI-assisted research improves their ability to identify and repair software weaknesses.
- Cybersecurity safeguards: Continued work on authorization, monitoring, and system isolation will remain important as model capabilities develop.
The next phase of AI cybersecurity will be measured not only by the volume of vulnerabilities discovered, but also by how effectively those discoveries contribute to safer software.
Conclusion
GPT-6 Cyber demonstrates how far AI-assisted security research has advanced.
OpenAI’s November 2026 findings involving 948 Linux privilege-escalation exploits and 81 previously unknown Firefox vulnerabilities show the growing ability of specialized models to investigate complex software.
Yet the research also highlights an unresolved operational challenge.
Finding a vulnerability does not automatically fix it.
Businesses, security researchers and software maintainers still need reliable validation, responsible disclosure and carefully tested patches.
As AI cybersecurity capabilities continue to develop, the effectiveness of these defensive processes will become increasingly important.
Follow Chapter Ninety’s technology news for cybersecurity developments, business insights, and clear analysis of the innovations shaping the digital economy.